 This is a free Easy-Rated challenge on TryHackMe that you can find here. Our instructions are just “Follow the leads and find who’s behind this operation.” That leads me to believe that we’re doing a little bit of Blue Team-type of work or at least some recon and OSINT intel digging about a fictitious hacker group. As you follow along, you will very likely see people who are ruining our fun by just posting flags in places you’ll go. Ignore those even if you see them and follow along the steps anyway. We’re building specific kinds of skills here and by short-cutting the flags, you’re only cheating yourself from learning. Enough moralizing, back to the challenge.
We get this instruction, “We got access to a hacker forum and found the info of our company on sale! All the info we have is in this post. Find any information related to the leader of the Sneaky Viper group.” and we find this message:
Full user database TryTelecomMe on sale!!!

As part of Operation Slither, we've been hiding for weeks in their network and have now started to exfiltrate information.
This is just the beginning. We'll be releasing more data soon. Stay tuned!

@v3n0mbyt3_

---
Task 1: The Leader
That just leads us to our first question: Aside from Twitter / X, what other platform is used by v3n0mbyt3_? Answer in lowercase.
This should be as easy as doing a search for that username, which seems pretty unique.
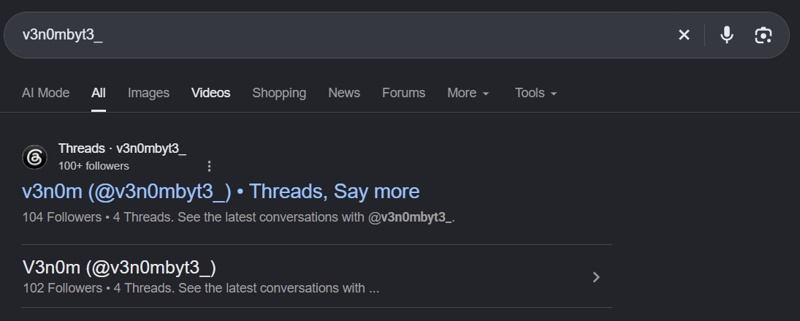
That gives us the answer, threads.
Next question is What is the value of the flag?
That’s not super helpful in and of itself, but if we use some context clues, I’m guessing that on Threads there is a post giving away the flag. If we go to the profile, we don’t see anything in the posts, so let’s check replies. There, we see what looks like a Base64 encoded string, VEhNe3NsMXRoM3J5X3R3MzN0el80bmRfbDM0a3lfcjNwbDEzcyF9. If I take that to Cyberchef and decode it, we get the answer… THM{sl1th3ry_tw33tz_4nd_l34ky_r3pl13s!}
Task 2: The Sidekick
Opening Task 2, we see this, “A second message has been made public! Our account in their forum was deleted, so we couldn’t get the operator’s handle this time. Follow the crumbs from the first task and hunt any information related to the second operator of the group.”
60GB of data owned by TryTelecomMe is now up for bidding!

Number of users: 64500000 Accepting all types of crypto
For takers, send your bid on Threads via this handle:

HIDDEN CONTENT
-----------------------------------------------------------------------------------------------------
You must register or log in to view this content
The first question is What is the username of the second operator talking to v3n0mbyt3 from the previous platform?
So, right where we were before in the replies on Threads, you can see conversations and our next answer, _myst1cv1x3n_
And our next question, What is the value of the flag?
So – again – not super helpful, but this seems like something we’ll find over in _myst1cv1x3n_’s profile. Turns out, that’s wrong. The only thing in the replies is that flag we got and used in task 1. Let’s search for _myst1cv1x3n_’s username and see if there are more sites out there linked to them. Didn’t find anything overt, but Threads accounts do have Instagram accounts connected to them. If we click the Instagram icon in the Threads profile, we’re taken to _myst1cv1x3n_’s Instagram. Some people have taken to commenting answers in the posts and that’s cheating. Let’s try to do this for real. If I look at each post, especially this one, we see they have a Soundcloud. If you work back to their profile and look at each song, we find a hint in the song called Prototype 2. The user left a Base64 encoded message in the description, VEhNe3MwY20xbnRfMDBwczNjX2Yxbmczcl9tMXNjbDFja30=. Decoding that gives us our answer THM{s0cm1nt_00ps3c_f1ng3r_m1scl1ck}
Task 3: The Last Operator
This task says “A new post is up. Hunt the third operator using past discoveries and find any details related to the infrastructure used for the attack.” Our message is
FOR SALE

Advanced automation scripts for phishing and initial access!

Inclusions:
- Terraform scripts for a resilient phishing infrastructure
- Updated Google Phishlet (evilginx v3.0)
- GoPhish automation scripts
- Google MFA bypass script
- Google account enumerator
- Automated Google brute-forcing script
- Cobalt Strike aggressor scripts
- SentinelOne, CrowdStrike, Cortex XDR bypass payloads

PRICE: $1500
Accepting all types of crypto
Contact me on REDACTED@protonmail.com

---
Our first question is What is the handle of the third operator?
For this one, I assume we’re looking for someone else who might be interacting with one or the other or both of these two. I clicked through comments and didn’t find anything good. I then decided to look at followers and found this.
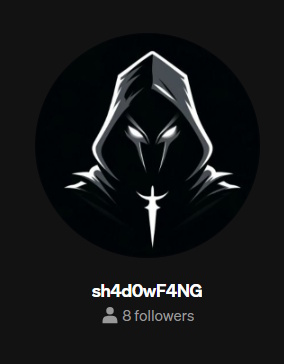
This gives us the answer, sh4d0wF4NG
What other platform does the third operator use? Answer in lowercase.
Okay, let’s search that user.
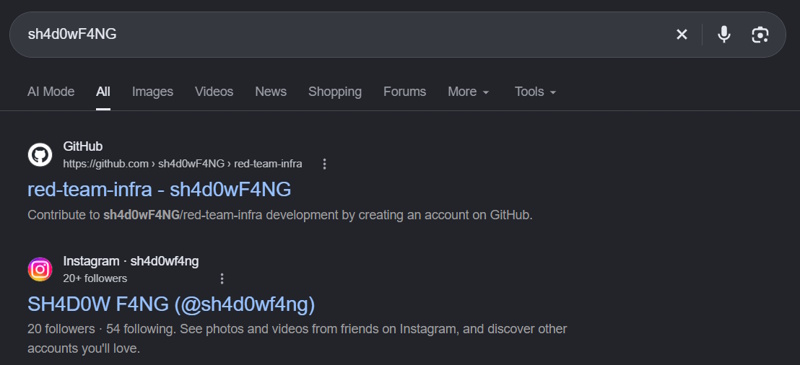
Our answer then is github.
What is the value of the flag?
I’m guessing we need to go digging in the GitHub of this person to find it. There are 3 repos, two are forks and one is their own. I decided to focus on the non-forked one first. However, it wouldn’t be crazy to expect that there was some change to one of the forked ones with our answer in it. I looked at all of the files first and didn’t see anything big. This repo only has 9 commits, so I looked at all of the diffs. This is a VERY FAVORITE trick in these kinds of CTFs. I ended up finding what I wanted in commit 90224ec. It was also in a diff that didn’t want to load. You had to click to load it since it was so large. There is a section that says
  "outputs": {
    "shadow-password": {
      "value": "VEhNe3NoNHJwX2Y0bmd6X2wzNGszZF9ibDAwZHlfcHd9"
      "type": "string"
    }
  },
That shadow-password value is a Base64 encoded value that decodes to our flag: THM{sh4rp_f4ngz_l34k3d_bl00dy_pw}
And there we go! All done.
